- Last Update05-Nov-2026


- Tweet
-
Google dismantles a network exploiting 1.3 million TV devices
Jordan News
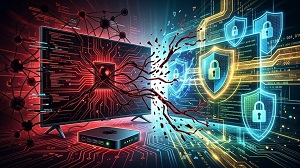
Google has announced the dismantling of a massive electronic network that exploited more than 1.3 million Android-based television devices, accusing a Chinese company of deliberately installing malicious software on its devices and selling access to them to cybercriminals.
Malware infecting Android devices is not a new phenomenon. However, a recent report from Google reveals a large-scale security threat, after the company managed to dismantle a huge network of compromised devices that turned more than 1.3 million Android-based television receivers into tools for exploitation by cybercriminals.
Unlike typical cyberattacks, which usually occur when users download suspicious apps from the internet, in this case the malicious software was pre-installed on the devices by the manufacturer itself.
According to a report published by Google's threat intelligence group, the company responsible for these devices is the Chinese firm VideoStrong Technology.
Google said it has cut ties with the manufacturer and barred it from developing or supplying software for devices officially approved to run Android.
How the malware worked
The network, known as "XCB," relied on a software backdoor planted directly in the firmware that controls the device's operation.
This backdoor allowed additional malicious software to be downloaded as soon as the device was switched on, without the owner's knowledge or consent.
Google said VideoStrong was selling access to infected devices to cybercriminal groups, who exploited them in a range of activities, including advertising fraud and data theft, as well as routing internet traffic through users' home connections.
The company explained that the problem is not limited to malware that can be deleted. The backdoor built into the device's system allows the malware to be downloaded again automatically upon restarting, even if the user succeeds in removing it.
Google's discovery of the vulnerability was not limited to television sets. It also found the malware in remote healthcare devices, karaoke machines and digital signage equipment.
In a post on X dated November 2, 2026, Google's cloud security unit announced that the company and its partners had disrupted the XCB network and cut off criminal groups' access to more than 10 million additional devices.
It noted that the attack did not rely on a traditional breach from outside, but on a manufacturer concealing a backdoor within its devices and then selling access to them to cybercriminals.
What happens to infected devices
Google worked with specialized cybersecurity companies and Japan's National Police Agency to disable the servers and infrastructure used to manage the network.
The company said dismantling the infrastructure that the criminal groups linked to the network rely on may also cut their access to at least 10 million other devices that were previously compromised.
However, shutting down the servers does not necessarily mean removing the malware already present on the devices, as it may continue to operate even after its connection to the network's infrastructure is cut.
Following the incident, Google announced changes to its device verification procedures before granting official Android certification, aiming to strengthen its ability to detect similar threats.
It also advised users to buy devices from trusted manufacturers and to keep "Google Play Protect" enabled to help detect malicious apps and software.
As for users of devices produced by VideoStrong Technology, Google advised them to disconnect their devices from the internet and consider replacing them with devices from trusted brands, given the possibility that malware may remain in their systems even after the network has been disabled.
Latest News
-
 Melania Trump to host Ukraine, Russia 'representatives' at White House – statement
-
 US strikes Iranian island — media
-
 King inaugurates 20th Parliament’s third ordinary session, delivers Speech from the Throne
-
 Safadi, Arab counterparts discuss regional developments, coordination
-
 Hassan reaffirms government commitment to Royal directives, modernisation agenda